Cybersecurity that shows up.
How we've helped to protect industries like yours.
 Education
Protecting a university's network against both hackers and a student workforce.
Read more → Government
Helping a Virginia municipality discover a dangerous backdoor.
Read more → Healthcare
An IT team of one quickly takes control of 400 vulnerabilities.
Read more → Aviation
A resilient and compliant digital infrastructure is the gateway to smooth airport operations.
Read more → Finance
Validating wireless security across two branches of a regional credit union.
Read more →Others sell a tool and wish you luck. We are the team that operates it.
- × Sells you a license, ships you a dashboard.
- × Alerts route to your team at 2 AM.
- × "Please open a ticket" is the response plan.
- × Audit defense? Not in the SOW.
- ✓ Humans watching your environment every hour.
- ✓ The analyst who investigated you knows you.
- ✓ Containment, not just detection.
- ✓ AuditArmor in the contract, not a slide deck.
Products are necessary but not enough. The EDR sitting on your endpoints is only as good as the analysts watching it at 2 AM. We are those analysts.
A complete cybersecurity practice.
Managed Security
Ongoing protection
24/7 eyes on glass. Our SOC, our analysts, your environment.
- ▸ SOC-as-a-Service. 24/7/365 from Assura's own SOC. Not white-labeled, not outsourced.
- ▸ Managed Detection & Response. We don't just alert. We contain.
- ▸ Advanced XDR Tooling. Stellar Cyber Open XDR — AI-driven correlation across your full stack.
- ▸ Threat Hunting & Intelligence. Proactive pursuit of what evaded the tooling.
- ▸ Incident Response & Forensics. When the worst happens, we show up.
- ▸ Log Management & SIEM. Centralized telemetry, retention, and search. Audit-ready.
- ▸ Security Awareness Training. The #1 attack vector is your people. We train them.
- ▸ Multi-Factor Authentication. Rollout, enforcement, and phishing-resistant MFA done right.
Offensive Security
Find it before they do
Real attackers. Real methodology. Findings you can fix before Monday.
- ▸ Password Audit. Weak, reused, and breached creds surfaced before attackers find them.
- ▸ Network Pentests. External, internal, cloud, and WiFi. Real methodology, not a scanner dump.
- ▸ Social Engineering. Phishing, vishing, pretext. Your people are target #1.
- ▸ Physical. Badge cloning, tailgating, drop boxes. Locks beat logs.
- ▸ AI. Prompt injection, model manipulation, the new attack surface.
- ▸ PTaaS. Continuous offensive testing, not an annual snapshot.
- ▸ VMaaS. Risk-prioritized vulnerability management with expert guidance.
- ▸ CTF Events. Capture-the-flag exercises to train and sharpen your team.
Governance, Risk & Compliance
Compliance that holds up
Policies, audits, and leadership. Backed in writing by AuditArmor.
- ▸ HIPAA · PCI-DSS · CMMC. All levels, with remediation, not just gap reports.
- ▸ SOC 2 · ISO 27001 · NIST. We hold ISO 27001 ourselves. We know the work.
- ▸ FedRAMP · CCPA · State Reg.. Federal and state frameworks.
- ▸ Virtual ISO (vISO). Fractional CISO leadership without the $300K salary.
- ▸ Risk Assessments. Threats, gaps, prioritized remediation.
- ▸ Policy & Procedure Development. Custom policies built for your environment, not templates.
- ▸ Third-Party Risk Management. Vendor and supply chain risk, assessed and tracked.
- ▸ DRaaS & Continuity Planning. Disaster Recovery as a Service and business continuity planning. Resilience when systems go dark.
AuditArmor®
It's in the contract, not a marketing slogan. No other firm our size offers this, because most aren't confident enough in their work to back it.
People who actually answer the phone.
Cybersecurity is a people business dressed up as a tech business. Every engagement is anchored by named humans, not a ticket queue, not a chat bot, not an offshore tier-1. The analyst who triaged your last alert knows your environment. The consultant who built your policies will sit next to you in the audit.
- → No A-holes Allowed. Talent matters. Character matters more.
- → Eat Our Own Dog Food. If we wouldn't trust it ourselves, we won't recommend it.
- → Sweat the Details. The 1% is what attackers find.
- → Walk the Talk. Our own SOC. Our own ISO 27001. No exceptions.
- → Own the Outcome. AuditArmor is what ownership looks like in writing.
- → Always Learn from a Good Disaster. Every incident is a teacher.
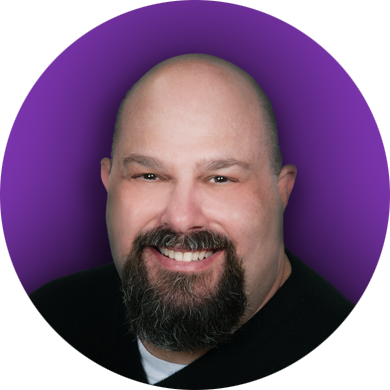
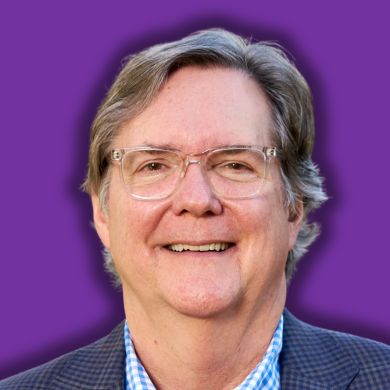
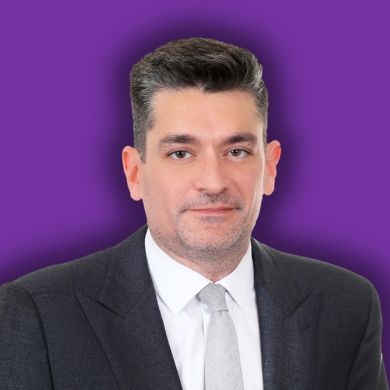
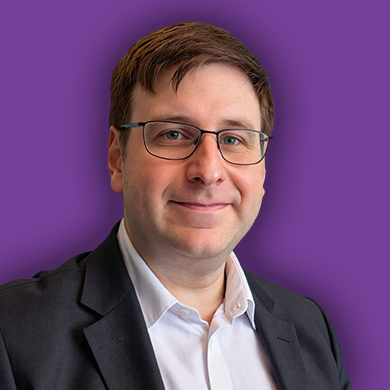
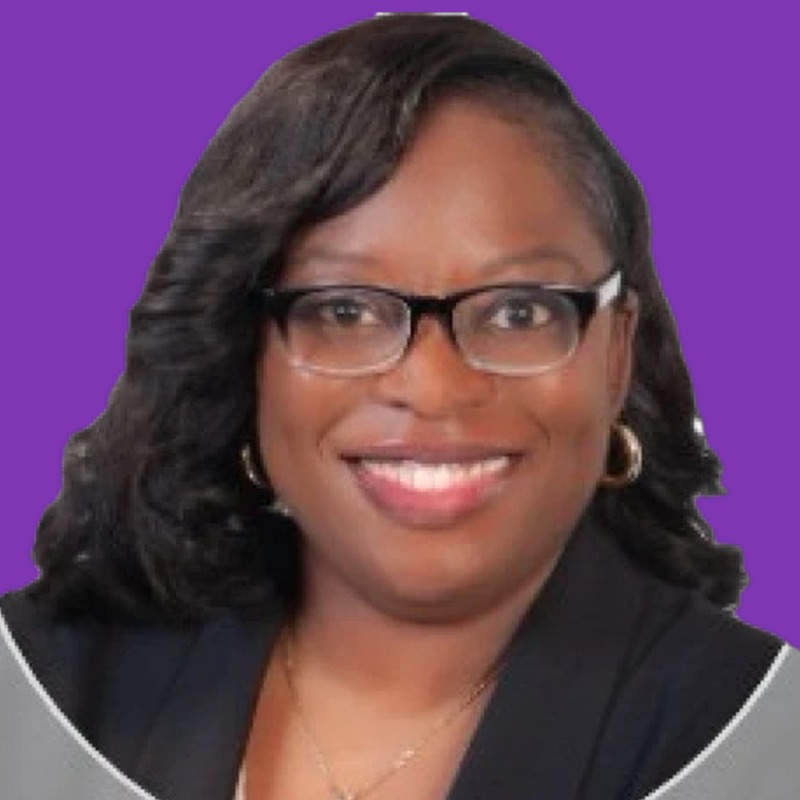
The leadership team behind our promises.
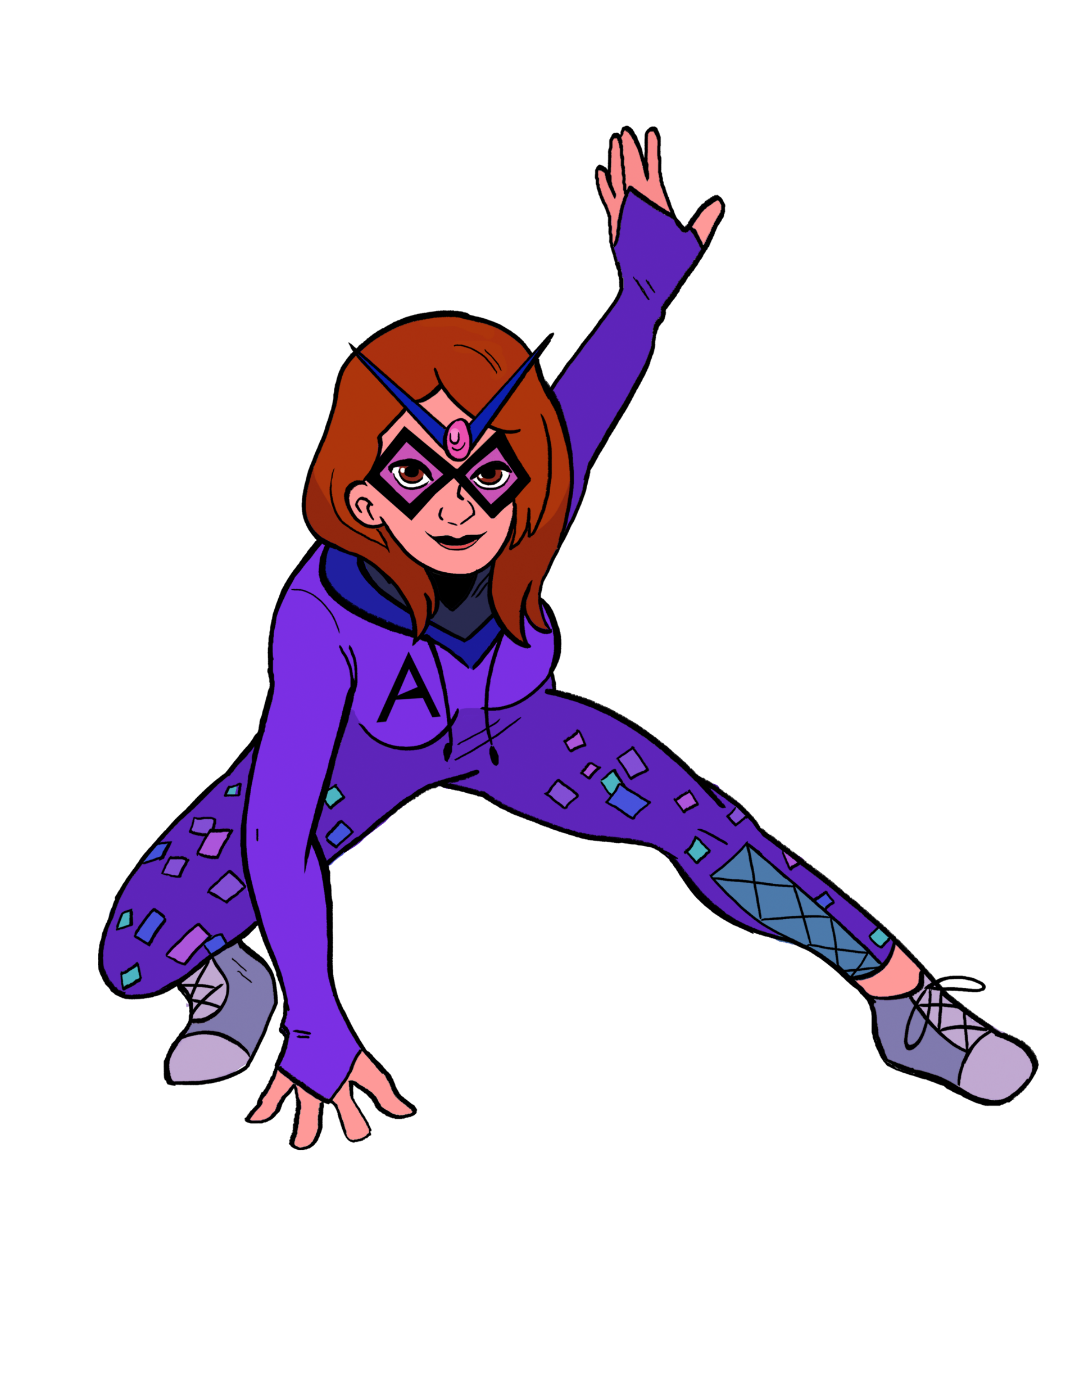
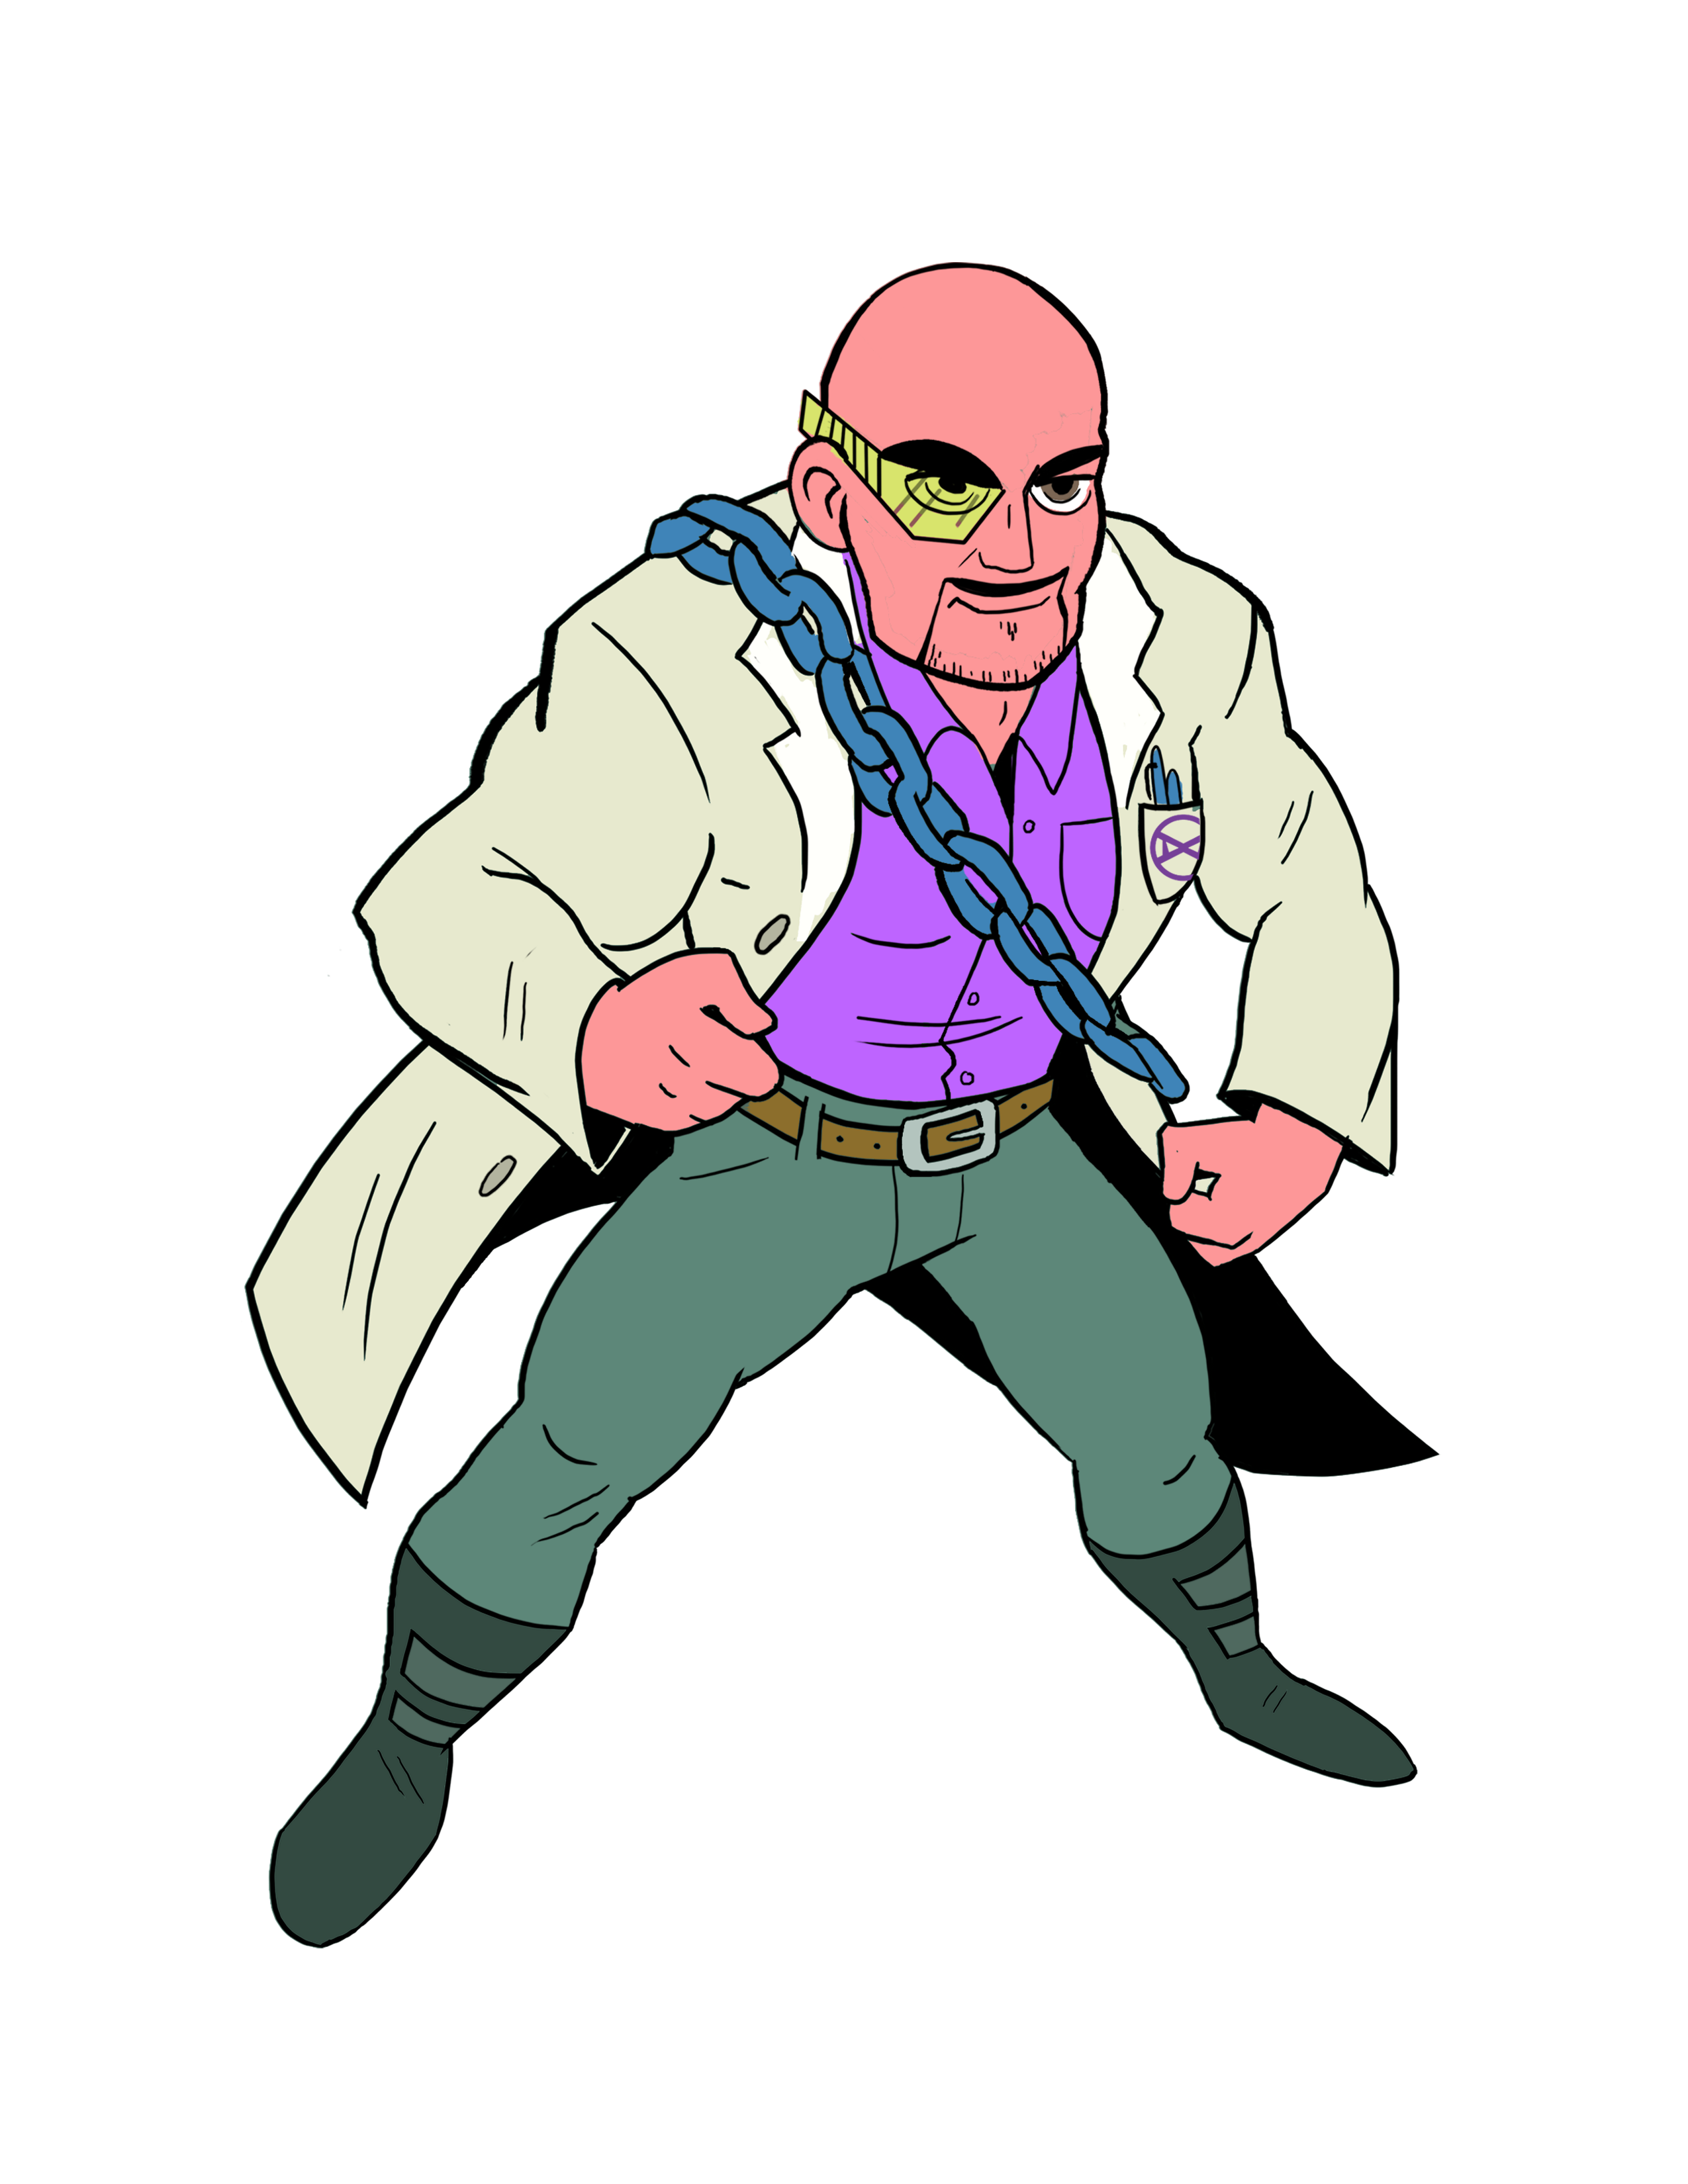
Every one of our ~50 employees has a superhero persona they transform into, a reminder that defending the mission takes more than a job title.
Hover over a leader to meet their alter ego.
If your data is worth protecting, we have probably worked with someone in your space.
Democratizing Cybersecurity
Let's have a real conversation.
30 minutes. No pressure. We'll tell you honestly whether we're the right fit, and if we aren't, we'll tell you who is.
richmond, va · founded 2007 · ~50 employees · iso 27001 certified